We've implementend some new anti scraping filters. If you can't reach chaos.social please send us a mail. #mastoadmin
mastoadmin

Today we're sharing additional guidelines about our Trade Mark Policy based on community feedback that we received.
The new guidelines, and more background about these changes, are available on our blog:
https://blog.joinmastodon.org/2026/08/sharing-guidelines-about-mastodons-trade-mark-policy/
#Mastodon #Fediverse #SocialWeb #FediDev #MastoDev #FediAdmin #MastoAdmin

We just released Mastodon v4.7.5, v4.6.11, v4.5.21 and v4.4.28.
They fix multiple high severity security issues. We encourage admins to update as soon as they can.
Full release notes and update instructions are available on the GitHub releases page.
Upgraded this Mastodon instance from 4.7.5 to 5.0.0-beta.1. Some sneaky version upgrades necessary, but I made it through. Lost the Tangerine UI, but not worried about it right now.
Don't know if this was just me, but after the update I wasn't able to get to the Admin areas without logging out and back in again on my Admin account.
➡️ https://about.iftas.org/2026/09/11/boom-protocol-spam/
the page linked above will re-post tips, tricks, guidance to combat the #bpSpam wave impacting many service providers.
#BoomProtocol #BoomProtocolProbe #Spam #FediAdmin #MastoAdmin #PeerTubeAdmin #FediMods #Mastomods
Edited 63d ago
RE: https://mastodon.social/@MastodonEngineering/117553453842624500
Happy security patch release day!
Seems we've another high severity security patches released today, be sure to patch your servers.
Our instances have all been upgraded to v4.7.5.
Have a great day y'all 👋
The first beta version for Mastodon 5.0 is now available!
After testing it on mastodon.social for a few weeks, we believe that this version is stable enough to be deployed by others, so if you like testing our new things feel free to install this beta version and report any bugs your find on GitHub or our community forum (https://community.joinmastodon.org/)
We expect the final release to happen within the next 2-3 weeks.
Release notes and upgrade instructions here: https://github.com/mastodon/mastodon/releases/tag/v5.0.0-beta.1
We just released Mastodon v4.7.2, v4.6.8, v4.5.18 and v4.4.25.
In addition to several bugfixes, they disable HEIF processing to avoid a known critical security issues. We encourage server administrators to update as soon as possible.
Full release notes and update instructions are available on the GitHub releases page.

If you're running a public Mastodon server, it's really important that you have a plan for closing down gracefully *even if you have no intention of closing down*.
Having a plan in place means your members don't have to worry about your server suddenly disappearing, as they know they will get plenty of warning if it happens.
Here's a step-by-step guide to closing a Mastodon server gracefully (and much of this applies to any Fedi server):
🏡 https://fedi.tips/closing-your-mastodon-server-gracefully/

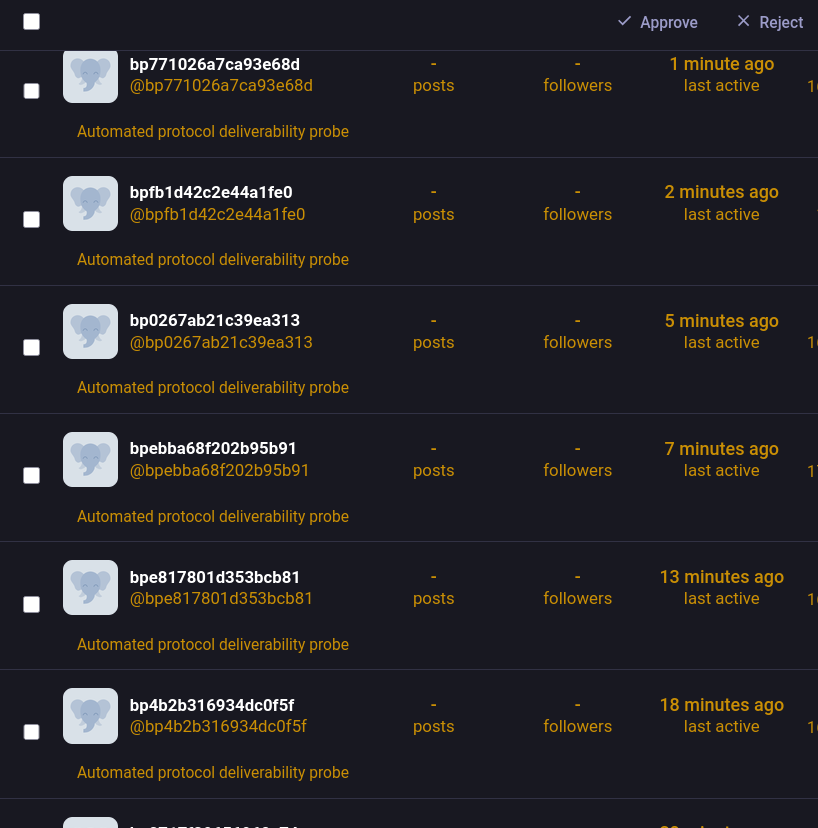
Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet.
On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave.
Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything.
The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth.
So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client.
If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include:
location = /api/v1/accounts {
  limit_except GET {
    deny all;
  }

  try_files $uri @proxy;
}
This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
Mastodon updated to v4.7.2, a critical security update. Is anyone else surprised that you don't have to run the bundle / yarn / RAILS_ENV steps in the last few patches? A happy surprise for me!
Is there a way to block registrations from any e-mail that has a subdomain in it? #AskFedi #MastoAdmin
Poll for Mastodon administrators *who are not using containers/Docker* : how are you installing Ruby?
If other, please reply to explain how you do it, and why.
For context, we are looking at reducing the number of Ruby versions supported by Mastodon to reduce our maintenance burden (like supporting only Ruby 4.0 in the next version) and want to better understand the impact of such a decision.
Options: (choose one)

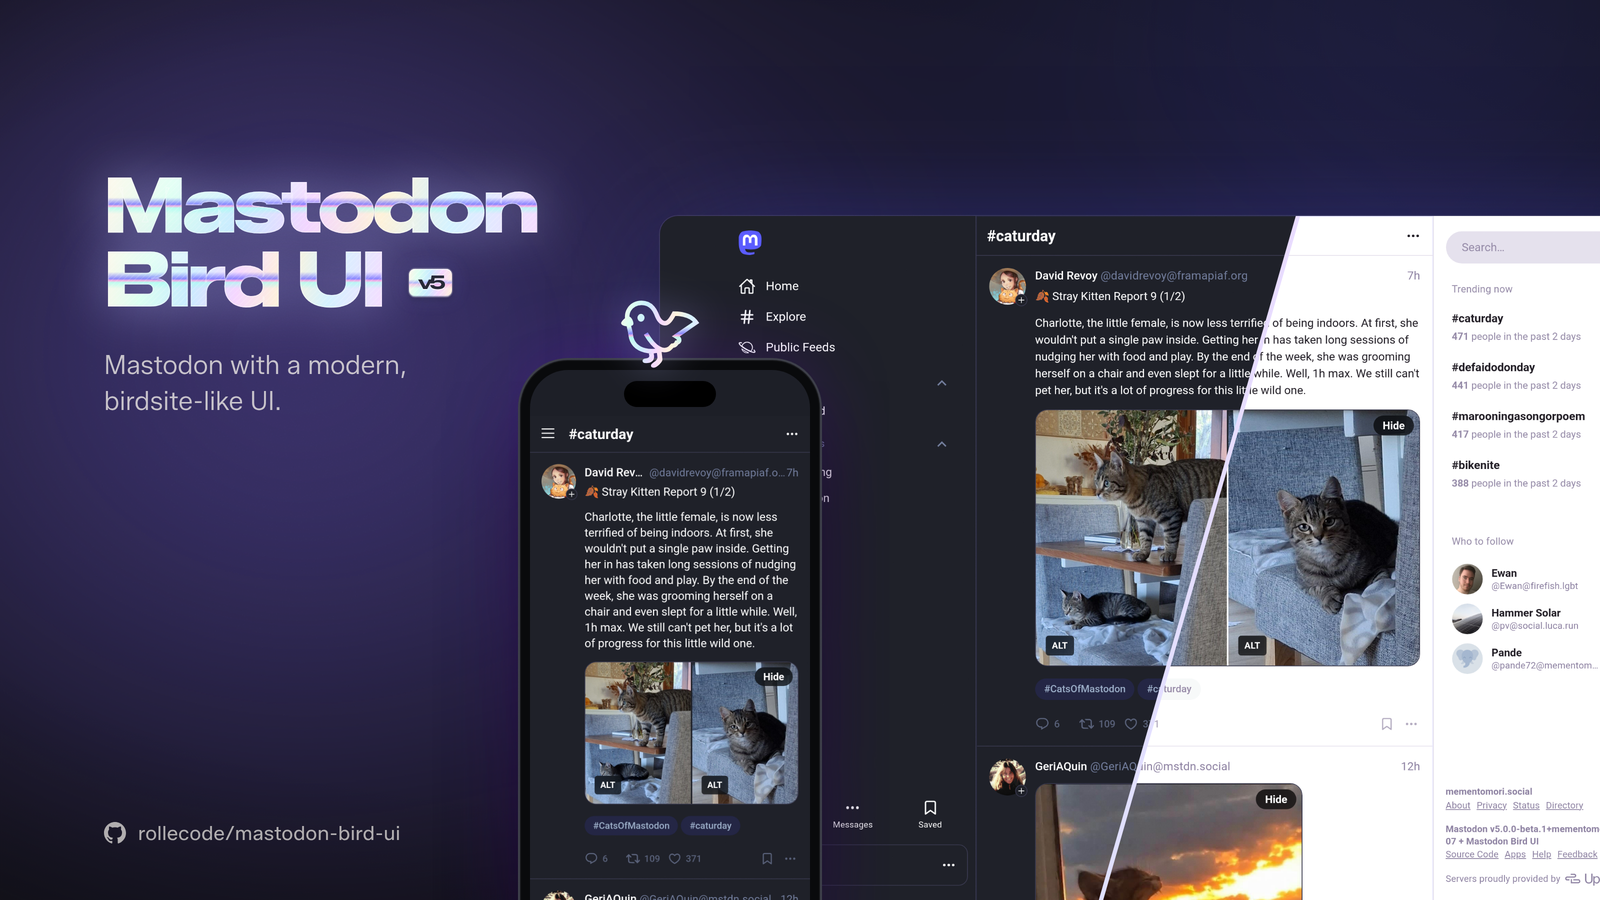
🐦⬛ Mastodon Bird UI 5.0.0-beta.1-2026-11-08 (nightly) is out. This is Bird UI rebuilt for Mastodon 5, the new 5.0 design that is now in beta.
The nightly follows Mastodon 5.0.0-beta.1. If you are on Mastodon 4, stay on 4.7.3-2026-10-11 from the main branch.
New:
- Rewritten from scratch for the Mastodon 5 design
- Micro-interactions, likes and boosts are whimsical
- Notifications, content warnings, link cards and thread lines look like they did on Mastodon 4
- Follows Mastodon's own light, dark and high contrast settings
- A darker, blurred backdrop behind the composer and every popup
- A new install script for Mastodon 5, or paste dist/mastodon-bird-ui.css into Custom CSS
- The star favorite, light and language variants are no longer supported
You can see it live at https://mementomori.social.
Release notes and full changelog: https://github.com/rollecode/mastodon-bird-ui/releases/tag/5.0.0-beta.1-2026-11-08
We are aware of an ongoing wave of subscription spam throughout the fediverse.
We are investigating avenues to mitigate this, but they will likely involve deep changes in the sign-up flow that may break sign-up from existing applications.
In the meantime, you can find helpful resources at https://about.iftas.org/2026/09/11/boom-protocol-spam/
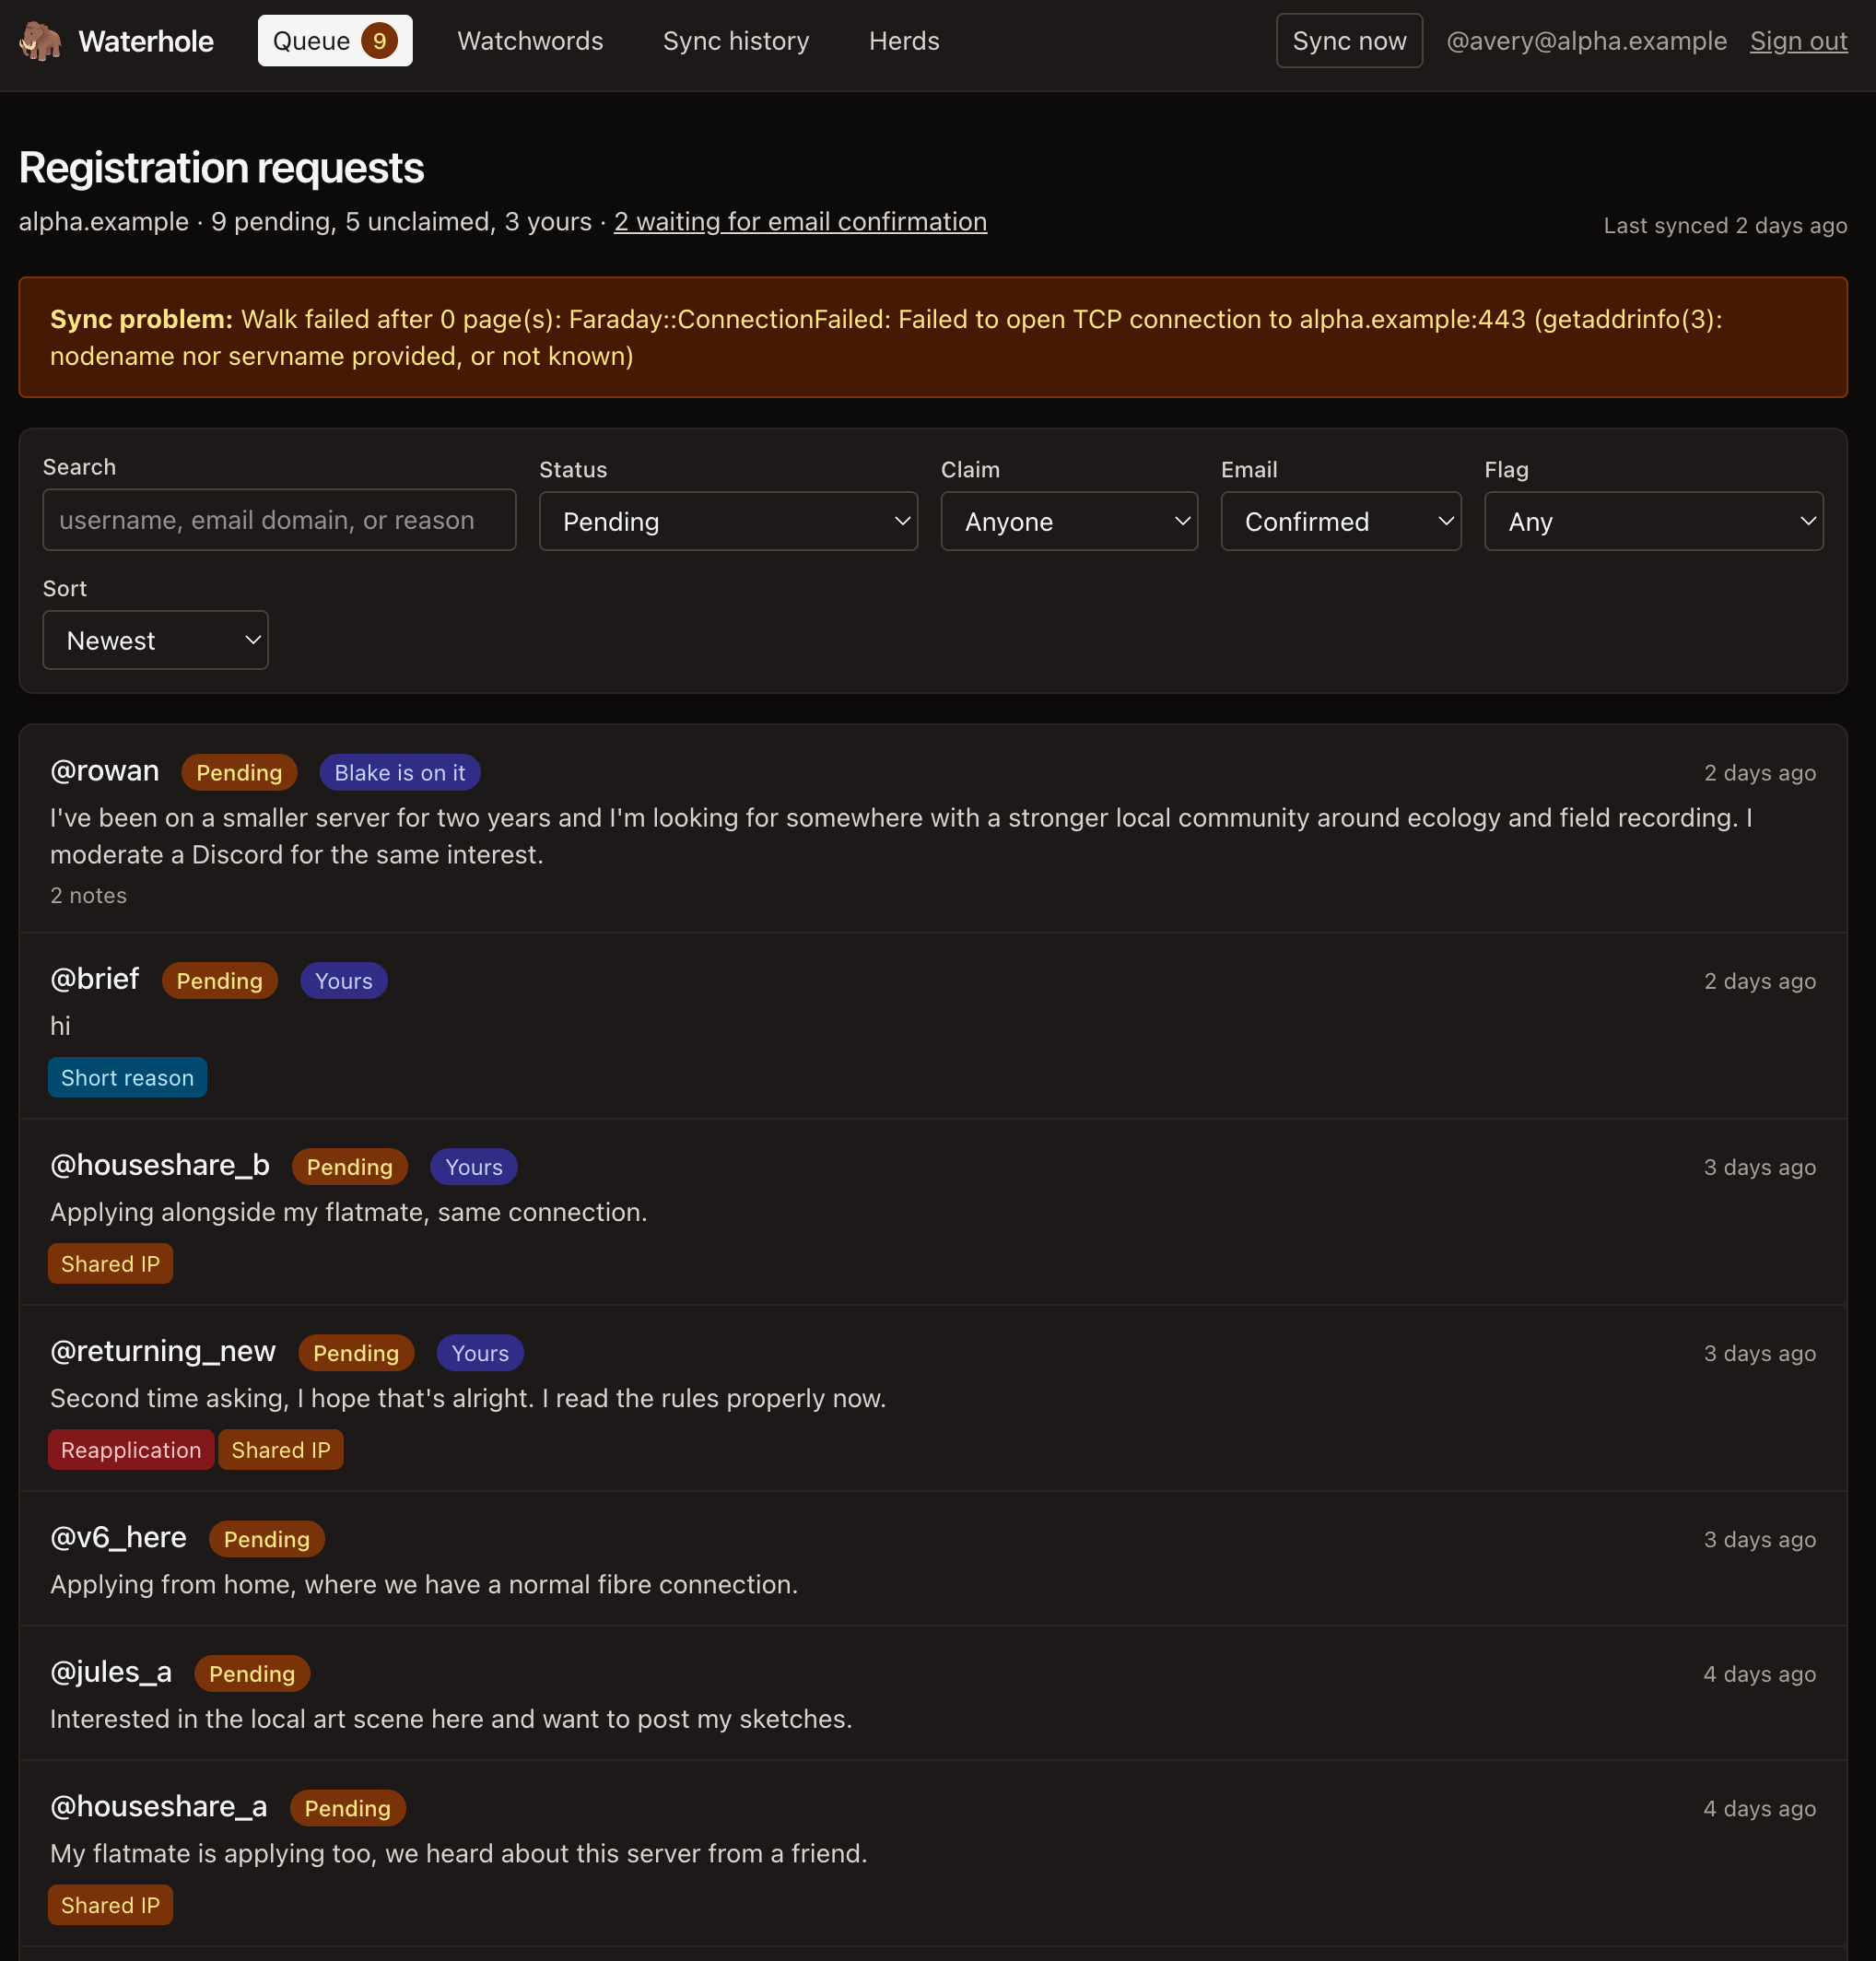
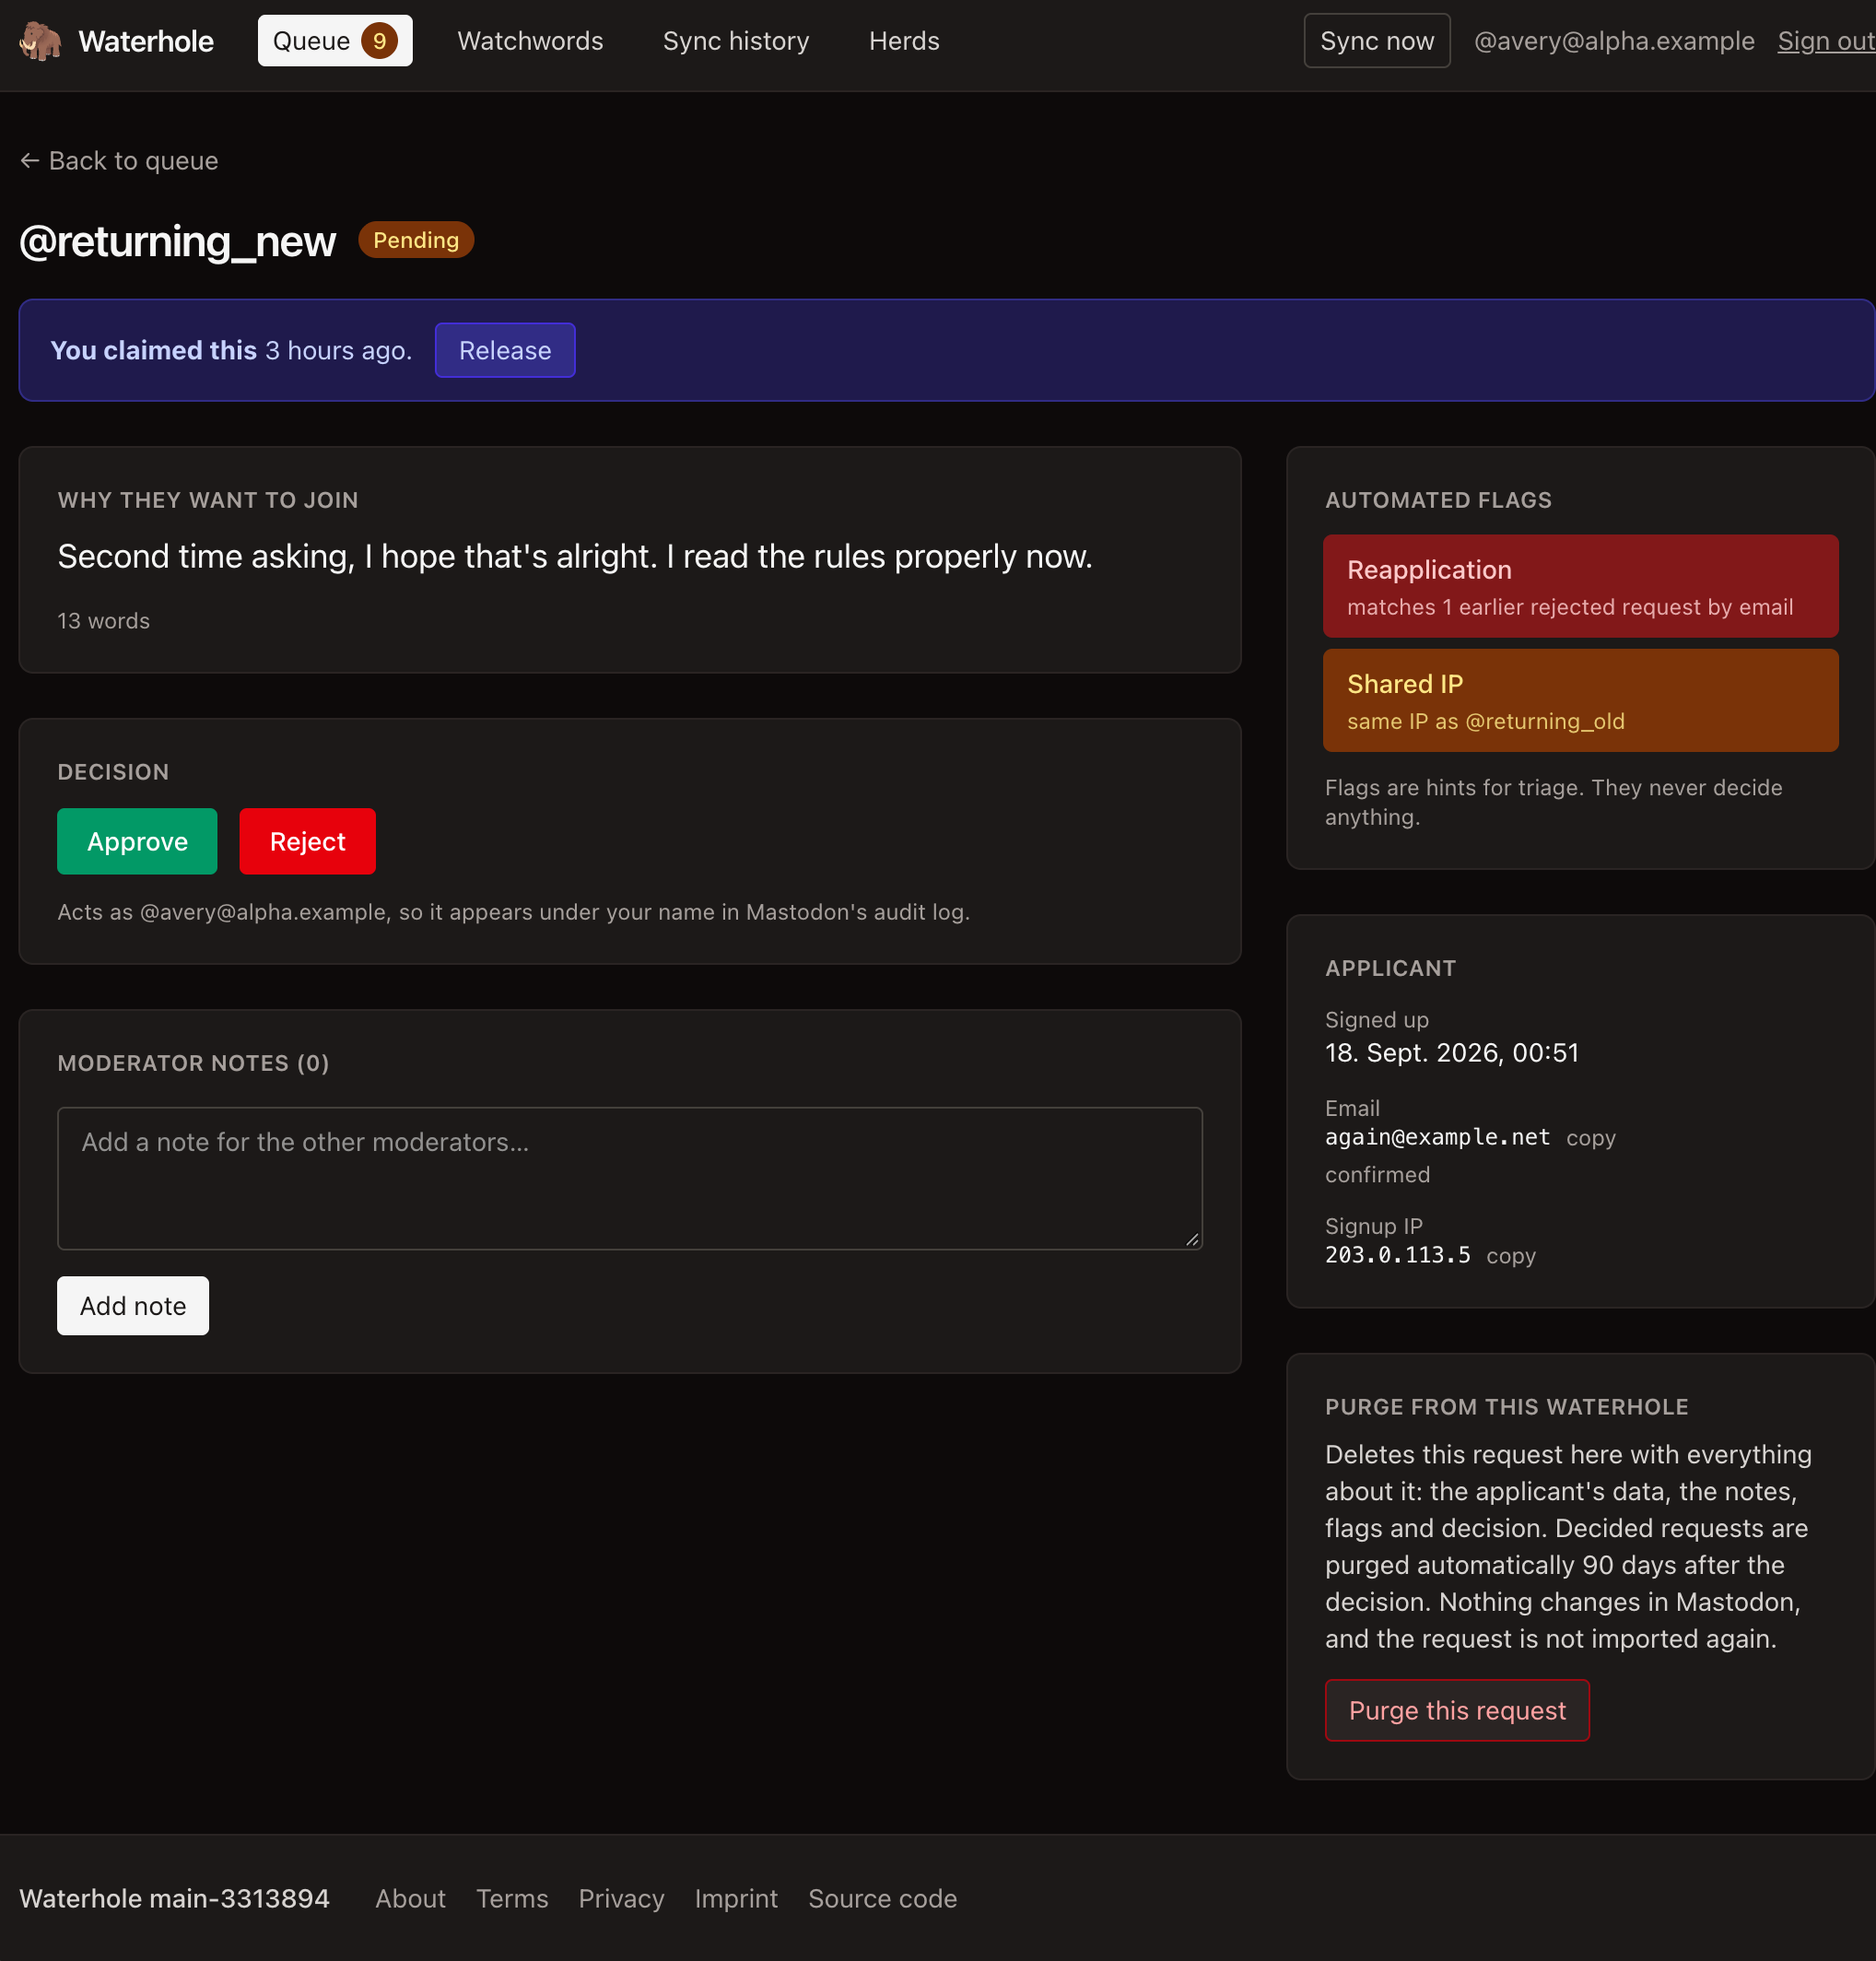
🦣 Herds that roam apart still come down to the same waterhole to keep watch together.
Introducing Waterhole: an open-source collaborative moderation tool built specifically for Mastodon instances that manually review and approve signups.
As Fediverse communities grow or spam waves hit, registration queues can quickly become overwhelming. Waterhole gives your moderation team a shared, real-time workspace to review applicants efficiently without compromising server autonomy or applicant privacy.
✨ Key Features:
• 📋 Shared Queues: Pending registration requests mirror directly into Waterhole. Claim requests, filter them by risk, and coordinate review status in real time.
• 💬 Team Discussion: Leave internal notes and discuss applicants collaboratively before deciding.
• 🔍 Proactive Signals: Automated checks highlight known throwaway email providers, datacenter IPs, Tor exits, templated join reasons, and burst signup patterns.
• 🛡️ Collective Defense: Opt-in cross-instance alerts notify you when the same spammer or bot pattern is prowling around multiple herds. Sharing only behavioral tracks and signals, never private applicant details.
• 🔒 Full Server Autonomy: Approvals and rejections are dispatched directly back to your instance via your Mastodon Admin API. No automated bans or AI decisions. You always keep complete control over who joins your community.
Waterhole is 100% free software under AGPLv3.
🔗 Connect your Mastodon instance to our Waterhole:
https://waterhole.toot.io/about
💻 Explore the source code, documentation, contribute, or self-host:
https://github.com/tootio/waterhole
#Mastodon #Fediverse #FediverseAdmin #MastoAdmin #OpenSource #SelfHosted #Privacy
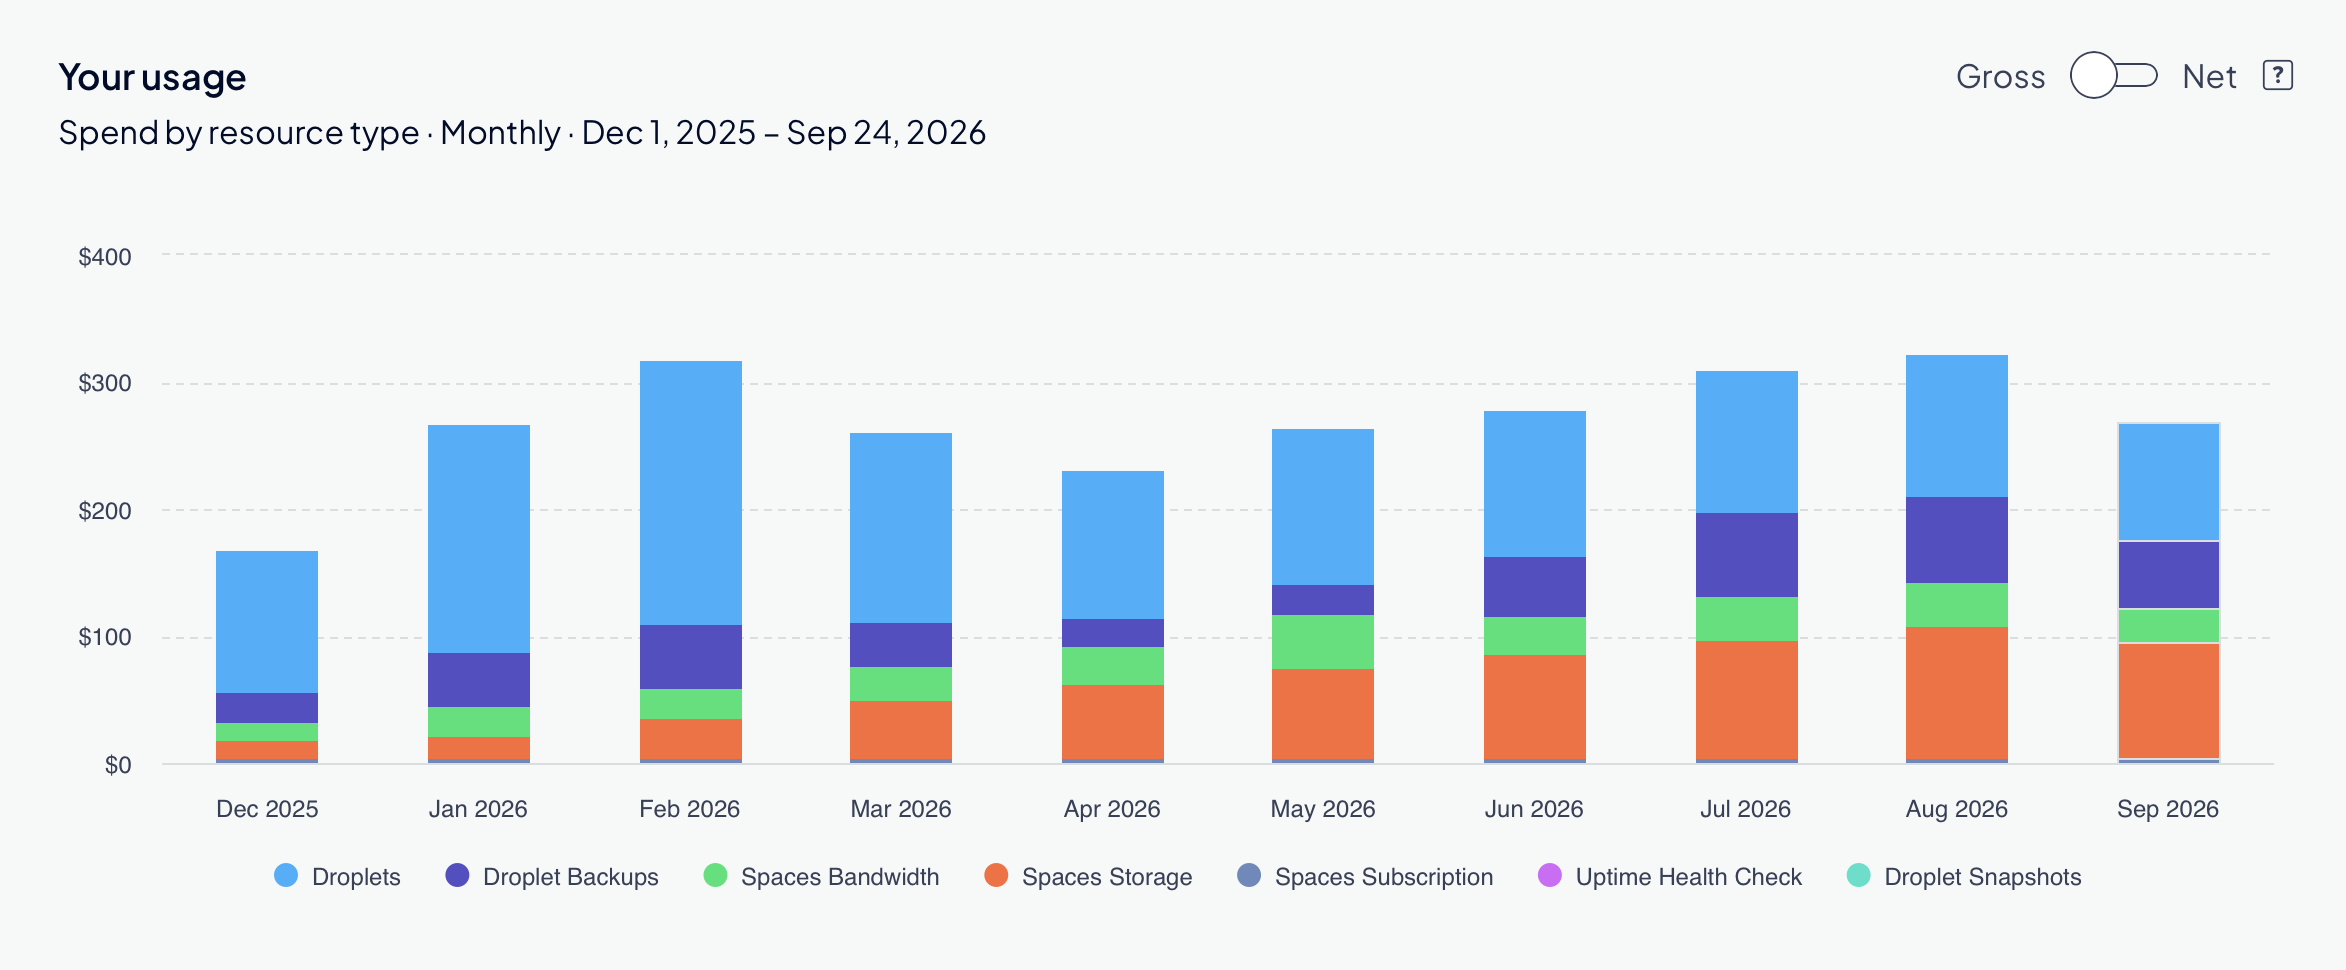
Huh—found out that a large amount of our infra costs have actually been due to Spaces storage. Time for some pruning! #mastoadmin
We just released Mastodon v4.7.3, v4.6.9, v4.5.19 and v4.4.26.
They contain many bugfixes in addition to updating some of our dependencies to fix security issues in those.
We recommend administrators to update when they can.
Full release notes and update instructions are available on the GitHub releases page.
 ⁂
I have a need to know how many text posts, images, and videos this Mastodon server gets in a month, local and remote (separately).
Or, from anyone else who has such data, what that looks like such that I can extrapolate a likely volume of all three stratified by local vs remote per e.g 1,000 active. If anyone has some handy dandy data and/or queries to run, I'd be extremely grateful.
chaos.social is now again up-to-date with mastodon v4.7.3 #mastoadmin

We are proud to announce that masto.nyc now has its own Android App! This is a fork from the mainline Mastodon that is a bit more tailored to the Masto NYC experience. Give it a try and we would love to hear any feedback!
https://play.google.com/store/apps/details?id=nyc.masto.android
- This app is complementary to the greater Fediverse app ecosystem. Using it isn't, and never will be a requirement to use masto.nyc
- iOS is also in the works
There are major account take-over problems happening right now on mastodon instances - all appearances are that the actor is using stolen passwords, probably from malware running on desktops. I've suspended hundreds of compromised accounts over the past 48 hours, but only two on mine.
If you run a mastodon instance, here is a postgres query I use to randomize the passwords of accounts that have been inactive for 6 months or more. It also removes logged in sessions. This doesn't lock people out, just makes them perform a password reset. Yes, I wish I didn't have to do this, but here we are. I hope it helps someone else.
BEGIN;
CREATE TEMP TABLE dormant_batch ON COMMIT DROP AS
SELECT u.id AS user_id
FROM users u
WHERE COALESCE(u.current_sign_in_at, u.created_at) < now() - interval '6 months'
AND NOT u.otp_required_for_login
AND NOT EXISTS (SELECT 1 FROM webauthn_credentials w WHERE w.user_id = u.id)
AND NOT EXISTS (SELECT 1 FROM oauth_access_tokens t
WHERE t.resource_owner_id = u.id
AND t.revoked_at IS NULL
AND t.last_used_at > now() - interval '6 months');
UPDATE users u
SET encrypted_password = '$2a$10$' || left(replace(gen_random_uuid()::text || gen_random_uuid()::text, '-', ''), 53),
updated_at = now()
FROM dormant_batch b
WHERE u.id = b.user_id;
UPDATE oauth_access_tokens t SET revoked_at = now()
FROM dormant_batch b
WHERE t.resource_owner_id = b.user_id AND t.revoked_at IS NULL;
DELETE FROM session_activations s
USING dormant_batch b
WHERE s.user_id = b.user_id;
SELECT COALESCE(y::text, 'total') AS last_seen_year, count(*) AS locked
FROM (SELECT date_part('year', COALESCE(u.current_sign_in_at, u.created_at))::int AS y
FROM dormant_batch b JOIN users u ON u.id = b.user_id) s
GROUP BY ROLLUP (y) ORDER BY y NULLS LAST;
COMMIT;
Edited 27d ago